Network and application penetration testing solutions: Securing Enterprise Infrastructure
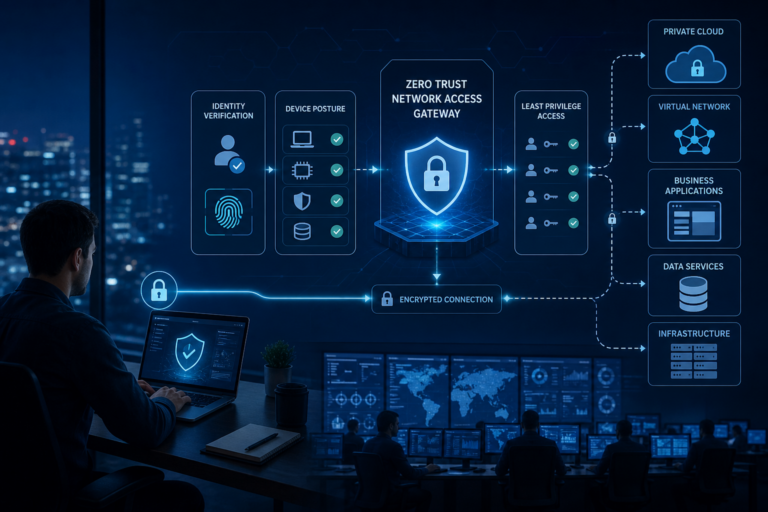
Cyber threats evolve rapidly, forcing organizations to proactively defend their digital assets. Consequently, businesses deploy network and application penetration testing solutions to identify vulnerabilities before malicious actors exploit them. Furthermore, these simulated attacks evaluate the effectiveness of existing security controls comprehensively. Therefore, enterprises can remediate weaknesses and fortify their infrastructure against sophisticated breaches.
The Strategic Value of network and application penetration testing solutions
Organizations cannot rely solely on defensive tools like firewalls and antivirus software. Attackers continuously develop new techniques to bypass perimeter defenses. Therefore, companies must adopt an offensive mindset to uncover hidden weaknesses. network and application penetration testing solutions provide this offensive perspective. Ethical hackers simulate real-world attacks to expose security gaps. Consequently, IT teams gain actionable insights into their actual risk posture. Furthermore, these solutions prioritize vulnerabilities based on potential business impact. Thus, security teams address the most critical threats first.
Proactive Threat Identification and Risk Mitigation
Reactive security measures cost organizations significantly more than proactive defenses. A single data breach causes massive financial and reputational damage. Therefore, identifying entry points before criminals discover them is crucial. Penetration testers exploit vulnerabilities safely to prove their impact. They might access sensitive databases or escalate user privileges. Consequently, executives understand the tangible risks facing the organization. This clear demonstration of risk secures budget for necessary remediation efforts. Thus, proactive testing transforms abstract security risks into concrete action items.
Core Components of network and application penetration testing solutions
A comprehensive security assessment evaluates multiple layers of an organization’s infrastructure. Attackers target any available weakness, from misconfigured routers to flawed code. Therefore, testing solutions must cover both network architecture and software applications. This holistic approach ensures attackers find no easy path into the environment. Consequently, organizations close gaps across their entire digital footprint.
Infrastructure and Internal Network Assessments
Network testing focuses on the underlying infrastructure supporting business operations. Testers examine firewalls, routers, switches, and servers for misconfigurations. Furthermore, they attempt to breach internal networks after gaining initial access. This simulates an insider threat or a compromised endpoint. They look for lateral movement opportunities and privilege escalation paths. Therefore, organizations learn how far an attacker could propagate through their systems. Consequently, network segmentation and access controls improve dramatically. Thus, infrastructure testing hardens the foundational layers of enterprise security.
Web and Mobile Application Security Testing
Applications often process highly sensitive data, making them prime targets. Testers analyze web and mobile apps for common vulnerabilities. They look for flaws listed in the OWASP Top Ten, such as SQL injection and cross-site scripting. Furthermore, they test authentication mechanisms and session management protocols. Testers attempt to manipulate application logic to access unauthorized data. Therefore, developers receive specific guidance on fixing insecure code patterns. Consequently, application security testing prevents devastating data leaks. Thus, securing the application layer protects both the business and its users.
Methodologies Driving network and application penetration testing solutions
The effectiveness of a penetration test relies heavily on the methodology employed. Different testing approaches yield different types of vulnerabilities. Therefore, organizations must select the right methodology based on their specific goals. A well-defined scope ensures the test delivers maximum value. Consequently, stakeholders receive relevant and actionable findings.
Black Box, White Box, and Gray Box Testing Approaches
Black box testing simulates an external attacker with no prior knowledge of the system. The tester must discover vulnerabilities independently. This approach provides a realistic view of an external attack surface. Conversely, white box testing provides the tester with full system access and source code. This deep analysis uncovers hidden logic flaws quickly. Gray box testing combines both approaches, offering partial system knowledge. Therefore, organizations often use gray box testing to balance depth and realism. Consequently, selecting the right approach tailors the assessment to specific threat models. Thus, methodological flexibility ensures a thorough security evaluation.
Evaluating Cloud and IoT Environments with network and application penetration testing solutions
Enterprise infrastructure now extends far beyond traditional on-premise data centers. Organizations adopt cloud computing and Internet of Things (IoT) devices rapidly. Consequently, the attack surface expands into new technological territories. Testers must understand cloud-specific misconfigurations and IoT hardware vulnerabilities. Therefore, testing solutions evolve to cover these modern environments. This evolution ensures security keeps pace with digital transformation initiatives. Consequently, organizations maintain robust defenses regardless of where their data resides.
Cloud Configuration and API Security Assessments
Cloud environments rely heavily on infrastructure as code and complex API integrations. A simple misconfigured storage bucket exposes millions of sensitive records. Therefore, penetration testers audit cloud configurations against strict security benchmarks. They attempt to escalate privileges within cloud identity and access management systems. Furthermore, they test API endpoints for broken authentication and excessive data exposure. Therefore, cloud testing secures the dynamic infrastructure powering modern applications. Consequently, businesses confidently leverage cloud agility without sacrificing security posture. Thus, specialized cloud assessments address risks unique to virtualized environments.
IoT Device and Hardware Exploitation
Connected devices introduce massive security challenges for enterprises. Manufacturers often prioritize time-to-market over robust security engineering. Consequently, IoT devices ship with hardcoded credentials and unpatched firmware. Penetration testers extract firmware and analyze it for cryptographic flaws. They attempt to intercept communication between the device and its controlling server. Furthermore, they test physical ports for unauthorized access. Therefore, organizations deploying IoT fleets understand the inherent risks involved. Consequently, they implement network segmentation to isolate vulnerable devices. Thus, IoT testing prevents compromised hardware from serving as a network bridge.
Compliance and Regulatory Alignment Through Testing
Many industries mandate strict cybersecurity controls to protect consumer data. Regulatory bodies require proof that organizations actively secure their systems. Therefore, penetration testing serves as a critical compliance tool. Auditors look for regular testing cycles and remediation reports. Furthermore, passing these tests proves due diligence in protecting sensitive information. Consequently, organizations avoid hefty regulatory fines and legal liabilities. Thus, testing aligns technical security with broader corporate governance requirements.
Meeting Industry Standards and Security Frameworks
Standards like PCI-DSS, HIPAA, and SOC 2 require periodic security assessments. network and application penetration testing solutions map their findings directly to these frameworks. Testers highlight exactly which controls fail to meet regulatory criteria. Therefore, compliance teams can address specific gaps before an official audit occurs. Furthermore, maintaining continuous compliance builds trust with clients and partners. Consequently, robust testing programs become a competitive advantage in regulated markets. Thus, aligning tests with industry standards streamlines the audit process significantly.
Integrating Testing into the Software Development Lifecycle
Security must not remain an afterthought checked right before deployment. Finding vulnerabilities late in development costs significantly more to fix. Therefore, modern organizations integrate testing directly into their software development lifecycle (SDLC). Developers run automated security scans during the coding phase. Furthermore, manual penetration tests occur at major release milestones. Consequently, security flaws are caught and fixed while the code is still fresh. Thus, shifting security left reduces technical debt and accelerates delivery.
Shifting Security Left in Development Pipelines
Integrating security into CI/CD pipelines requires specialized tools and processes. Dynamic and static application security testing tools run automatically on every commit. These tools catch common coding errors before they reach production. However, automated tools cannot replace human intuition for complex logic flaws. Therefore, manual penetration testing remains essential for major releases. Human testers chain multiple minor vulnerabilities together to create a critical breach. Consequently, combining automated scanning with manual testing creates a highly resilient pipeline. Thus, DevSecOps cultures prioritize continuous security alongside continuous delivery.
Choosing the Right network and application penetration testing solutions Provider
Not all security vendors possess the same level of expertise. Automated scanning tools alone do not constitute a true penetration test. Therefore, organizations must carefully vet potential security partners. A reliable provider employs highly skilled ethical hackers. These experts think creatively to bypass security controls. Furthermore, they communicate findings clearly to both technical and executive audiences. Consequently, selecting the right provider ensures a valuable and thorough assessment. Thus, due diligence during vendor selection guarantees a successful engagement.
Evaluating Expertise and Reporting Capabilities
Organizations should review a provider’s certifications, such as OSCP or CEH. These credentials prove a baseline of technical knowledge. Furthermore, buyers must request sample reports to evaluate quality. A good report provides clear step-by-step reproduction instructions. It also includes risk ratings and actionable remediation advice. Therefore, internal teams can fix issues quickly without confusion. The provider should also offer a retest to verify the fixes work. Consequently, comprehensive reporting and retesting close the security loop effectively. Thus, a strong vendor partnership extends beyond the initial testing phase.
FAQs
1. What are network and application penetration testing solutions?
They are specialized security services where ethical hackers simulate cyberattacks to uncover vulnerabilities in infrastructure and software.
2. How often should an organization conduct penetration testing?
Organizations should conduct tests annually at minimum, and additionally after major infrastructure changes or new application launches.
3. What is the difference between black box and white box testing?
Black box testing gives the attacker no prior system knowledge, while white box testing provides full source code and architecture access.
4. Do penetration tests help with regulatory compliance?
Yes, frameworks like PCI-DSS and HIPAA require regular penetration testing to prove adherence to strict data security standards.
5. Can automated tools replace manual penetration testing?
No, automated tools find common flaws quickly, but human testers are required to chain complex logic vulnerabilities together.
6. What happens after a penetration test is completed?
The provider delivers a detailed report with vulnerability findings and remediation steps, often followed by a retest to verify fixes.
Conclusion
Defending enterprise infrastructure requires a proactive and aggressive approach to vulnerability management. network and application penetration testing solutions provide the critical insights needed to expose weaknesses before malicious actors exploit them. By evaluating infrastructure, applications, cloud environments, and IoT devices, organizations gain a comprehensive understanding of their security posture. Furthermore, integrating these tests into the development lifecycle and compliance frameworks ensures continuous security alignment. Ultimately, investing in expert penetration testing solutions empowers businesses to remediate risks efficiently, protect sensitive data, and maintain operational resilience in an increasingly hostile digital landscape.