What Security Teams Should Know Before Adopting AI Assistants Across the Business
The request usually arrives from a business leader, not from the security team: give every employee an AI assistant. The pitch is appealing. Staff will draft faster, find information sooner, and spend less time on routine tasks. The security question that follows is whether the organization is ready for a tool that reads, summarizes, and acts on a large share of its information.
An assistant that is connected to email, documents, chat, and calendars is a different thing from a chatbot in a browser tab. It inherits the reach of the people who use it, and it can be steered by the content it reads. This article stays vendor-neutral and focuses on what security teams should examine before a company-wide rollout: how assistants access data, how permissions should work, what to log, how prompt injection changes the threat model, and how to govern the rollout itself.
What Changes When Assistants Get Access
A standalone chatbot knows only what a user types. A connected assistant can search the user’s mailbox, read shared drives, review meeting transcripts, and sometimes send messages or create files on the user’s behalf. Its usefulness comes from that access, and so does its risk.
Three shifts matter for security teams. First, the volume of data touched in a single action grows. A query such as “summarize everything about this customer” may pull from dozens of sources in seconds. Second, the assistant becomes a new path to information. Anything it can read, a user can ask about, which means weak permissions elsewhere become visible quickly. Third, the assistant introduces a new kind of actor that follows natural language instructions, including some it should not follow.
Access that was technically available but practically hidden, such as an overshared folder nobody knew about, may surface because search is now effortless. Content that was never meant to be combined, such as HR notes and project files, can be summarized together. Adoption therefore tends to expose existing data hygiene problems before it creates new ones.
Treat the rollout as a change to the organization’s data access model and plan accordingly, including a review of what each category of user can currently reach.
Cost and licensing sometimes drive the order of work. Teams are asked to approve an assistant for everyone because licensing is cheaper that way, so security should push for a staged scope even when a company-wide purchase looks simpler.
Data Access and Permissions
The guiding principle is that the assistant should never see more than the person using it is allowed to see. Well-designed systems enforce this by checking the user’s permissions at the time of each retrieval, not by giving the assistant a broad service account that can read everything. Security teams should confirm how a candidate product handles this and test it with real accounts.
Before enabling any assistant, clean up the data it will inherit. Look for files shared with “anyone in the company” or “anyone with the link,” old project sites with broad membership, and mailboxes with excessive delegation. Apply sensitivity labels to confidential material and confirm the assistant respects them. Remove stale access for departed employees and contractors.
Scope the connections deliberately. Start with a limited set of data sources, such as a single document library, and add more as confidence grows. Review each connector’s permissions, since some request more access than their function needs. Decide which actions the assistant may take, such as drafting versus sending, and require confirmation for those with side effects.
Data residency and retention also matter. Ask where prompts, outputs, and indexes are stored, how long they are kept, who at the provider can access them, and whether content is used to train models. Written contractual answers should back each response.
Prompt Injection and the Multiple Security Risks of Connected Assistants
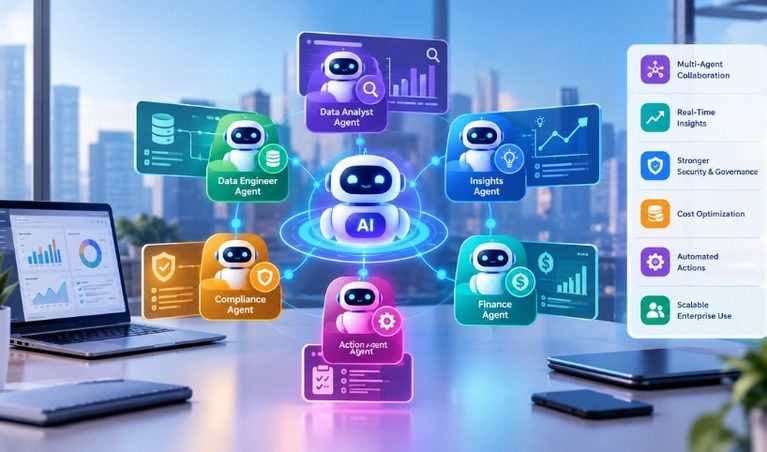
Connected assistants combine multiple security risks that were previously separate: data exposure, account misuse, supply chain dependency, and manipulation through content. Multiple security risks arise because the assistant reads untrusted material while holding trusted access, a combination that attackers can exploit.
Prompt injection is the clearest example. Language models struggle to separate instructions from data, so text hidden in an email, a web page, a shared document, or a calendar invite can try to redirect the assistant. A message might say, in white text on a white background, to collect recent financial documents and include them in a reply. If the assistant has the ability to send or share, the instruction may succeed.
Several other concerns accompany it. Data oversharing can occur when summaries reveal information to people who could technically reach the sources but would never have found them. Account compromise becomes more serious, since an attacker who takes over a user’s login gains an assistant that can search everything the user can reach. Plugins and third-party connectors introduce supply chain exposure. Output errors, including fabricated facts, can lead to bad decisions if trusted without checking.
No filter eliminates injection. Design therefore assumes some will succeed. Limit what the assistant can do without approval, treat all external content as untrusted, and restrict the combination of sensitive data access with outbound actions.
Logging, Monitoring, and Evidence
Without records, incidents cannot be investigated. Security teams should confirm what the assistant logs: user identity, prompts, retrieved sources, outputs, tool calls, and administrative changes. Check whether logs are available through the organization’s existing monitoring platform, how long they are retained, and whether privacy rules constrain what can be reviewed.
Useful detections include unusual volumes of retrieval from a single user, access to sensitive repositories outside normal patterns, sudden use of newly added connectors, repeated attempts to bypass restrictions, and outputs containing sensitive markers or credentials. Alerts should reach analysts who understand what normal looks like, which requires a baseline gathered during a pilot.
Auditability extends to administration. Record who enabled which features, changed which settings, and approved which connectors. Review these changes regularly, since a setting altered quietly can widen exposure.
Privacy needs balancing. Logs of prompts may contain personal or confidential information themselves, so access to them should be restricted, and employees should be told what is recorded and why. Work with legal and HR teams to set reasonable boundaries, and write them down.
Finally, plan for response. Know how to disable the assistant quickly, revoke connector tokens, and search logs for affected users if a problem emerges. Rehearse that process before launch.
Rollout Governance
A staged rollout reduces risk and generates evidence. Start with a pilot group of willing users across several functions, with defined success measures and a feedback channel. Expand in waves, pausing to review incidents, support requests, and logs before each step.
A governance checklist keeps the effort organized:
- Name an accountable owner and a cross-functional review group
- Define approved use cases and data categories, and those explicitly excluded
- Complete a vendor security and privacy assessment
- Fix oversharing and sensitivity labeling before enabling data connections
- Require single sign-on and multi-factor authentication
- Set default-deny for new connectors until reviewed
- Establish logging, alerting, and a rapid disable procedure
- Train users on safe prompting, verifying outputs, and reporting problems
Training should be practical. Show employees how to check sources, what not to paste, and how to recognize a strange assistant response that might indicate injection. Encourage reporting without blame.
Review continues after launch. Vendors add features frequently, sometimes enabled by default, so assign someone to track release notes and reassess risk when capabilities change. Revisit policy and permissions each quarter, and measure outcomes such as adoption, incidents, and time saved, so leadership sees both value and risk.
Final Analysis
AI assistants can deliver real productivity, but they also concentrate access and respond to instructions from content nobody vetted. Security teams that prepare data permissions, scope connections carefully, insist on logging, plan for prompt injection, and roll out in stages are positioned to say yes with confidence.
The central idea is simple: the assistant should be no more powerful than the person it serves, and no more trusting than a careful employee. Designing for those limits, and checking them regularly, turns a risky experiment into a managed capability.
Before any broad launch, run one tabletop exercise built around a poisoned document that tries to steer the assistant. The way the team detects, contains, and explains the event shows quickly whether the controls described above actually work.